Guide
What Is the SEC SDLC? Security at Every Stage
Build security into each software phase, from planning through ongoing care.
What is the SEC SDLC?
SEC SDLC means a secure software development lifecycle. It builds security tasks into the work of planning, designing, coding, testing, releasing, and caring for software. The goal is to find risks early and make safe choices part of daily work.
SDLC stands for software development lifecycle. A secure SDLC adds security goals, owners, and checks to the full SDLC. Teams can shape the steps to fit their product, but each step needs clear tasks and proof that those tasks were done.
For example, a team making an account service may set rules for sign-in and data access during planning. It can test those rules during coding and before release. The NIST Secure Software Development Framework offers practices teams can add to their own process.
A secure SDLC cannot promise software will have no flaws. It gives teams a steady way to lower risk, catch issues, and respond to new threats. Security becomes part of delivery, not a last-minute gate.
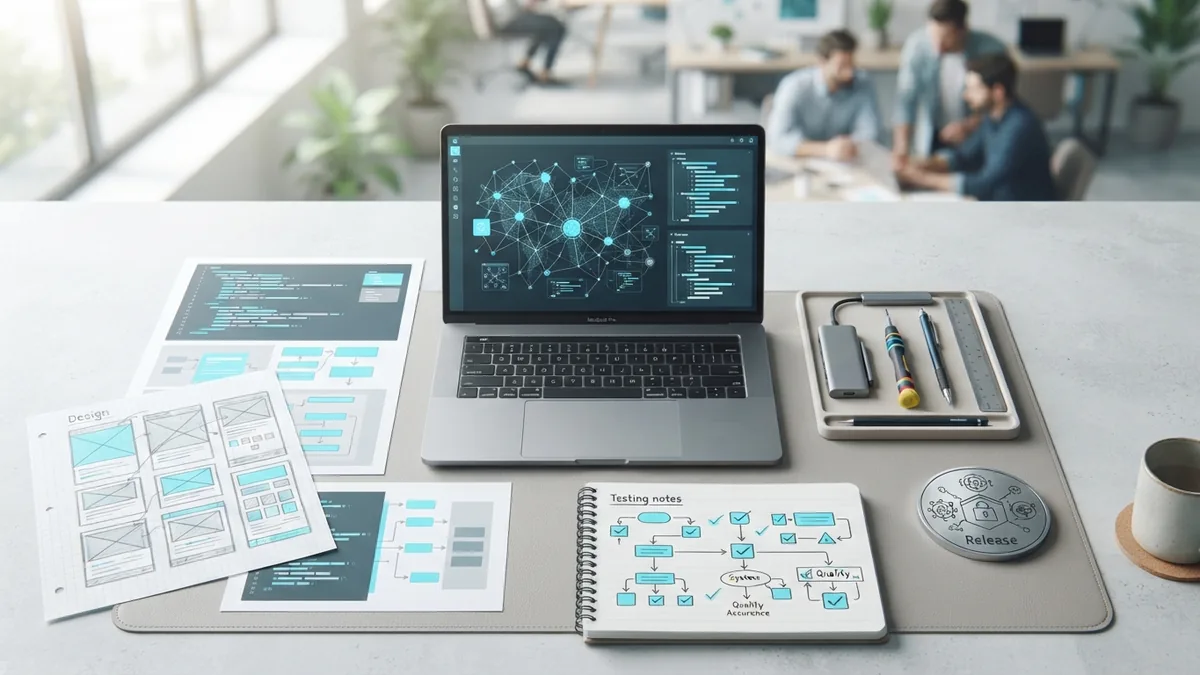
Key phases and activities in a secure SDLC
Teams may use different names for lifecycle phases, but the core work is much the same. Each phase should have a named owner, security tasks, and a way to check the result. This makes the activities of SDLC clear to both builders and reviewers.
- Plan: Define users, data, goals, and risks. Set the rules for who can approve key choices.
- Design: Map data flows and trust boundaries. Use threat modeling to find likely attacks and choose safeguards.
- Code: Follow secure coding rules, review changes, and scan source code. Track third-party packages and their known flaws.
- Test: Check features, access rules, and likely attack paths. Fix serious issues or record who accepted the risk.
- Deploy: Check release settings, limit access, and keep a rollback plan ready.
- Maintain: Watch alerts, patch flaws, and use incident response plans when issues arise.
Implementation in SDLC works best when teams start with a short list of risks. A service that stores payment data needs different checks from a public information site. Choose tests that match the data, users, and likely harms.
Quality assurance in SDLC should cover security as well as features. A test plan can name each check, its owner, its expected result, and its evidence. This makes release choices easier to explain and review.
Maintenance is not an afterthought. Teams should use incidents and new flaw reports to improve design and tests. The full SDLC continues for as long as the software remains in use.
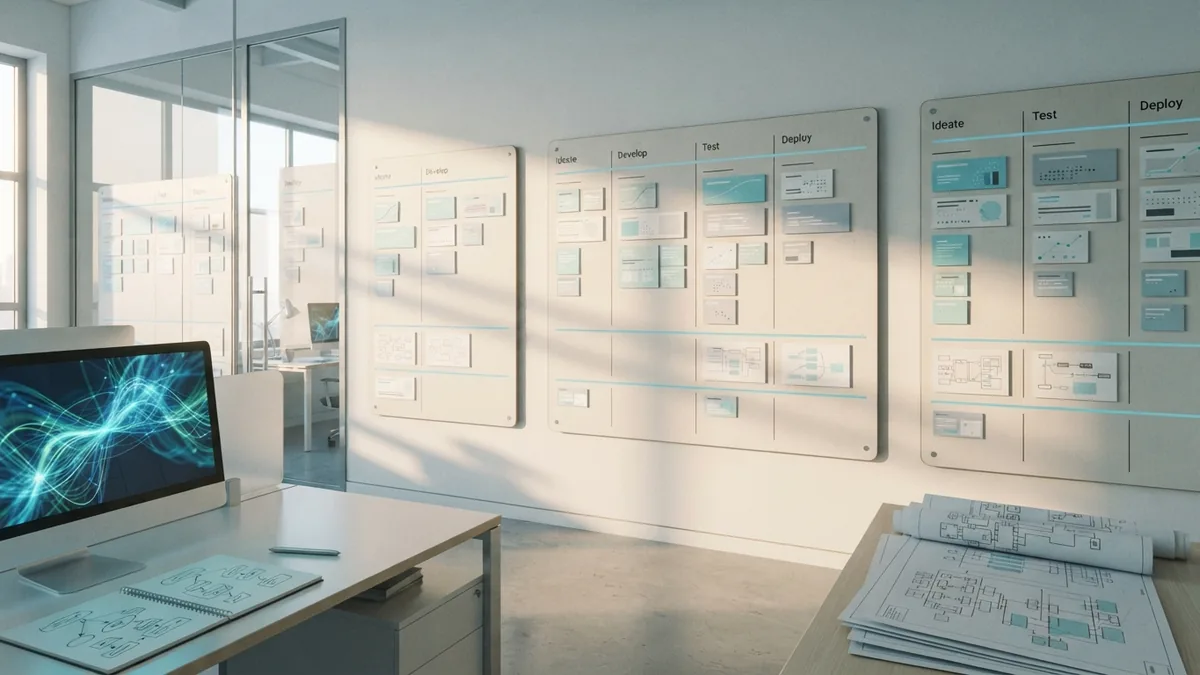
Methods of SDLC and their security trade-offs
Waterfall, Agile, and Spiral are common methods of SDLC. They differ in how work moves, how often teams review choices, and how they handle change. None removes the need to name risks and test safeguards.
Waterfall moves through set phases in order. It can suit work with stable needs, formal approval gates, or fixed records. A flaw found late can force costly changes, so teams should review threats and design choices before coding.
Agile breaks work into short cycles. Teams can add a security task to each cycle, such as checking a new access rule. This keeps tests close to the code they cover. Spiral SDLC repeats planning and risk review in rounds. It can fit large or uncertain work, but needs skilled risk review and clear records.
Incremental SDLC releases a system in useful parts. This lets teams test each part before adding more. Lean SDLC focuses on reducing waste, while adaptive SDLC makes room for changing needs. These approaches can support secure work when teams keep risk checks in each release.
Microsoft SDL is a set of secure development practices from Microsoft. Teams may also use security rules that fit their own tools and products. Whatever the method, set security gates based on risk, not habit alone.
Tools and automation for secure development
No single SDLC tool covers every security need. Teams often combine code checks, running tests, package review, secret checks, and work tracking. Pick tools that fit the build process and the risks of the product.
- Static code analysis: Checks source code for common flaws without running the program.
- Dynamic testing: Checks a running service for weak access rules and unsafe inputs.
- Package scanning: Finds known issues in outside code and helps teams plan updates.
- Secret scanning: Finds keys or passwords added to code by mistake.
- Build checks: Run tests when code changes and can stop a release when a key rule fails.
- Work tracking: Keeps risks, fixes, owners, and approvals linked to product work.
SDLC automation can run these checks each time a developer changes code. Start with checks that catch serious, common issues. Then tune alerts to reduce noise, since teams may ignore tools that report too many false alarms.
SDLC automation tools should support clear action. Each finding needs a risk level, an owner, and a due date. Keep a human review for major risks and any release exception.
Some teams connect security work with DevOps, which joins software building and operations work. SDLC and DevOps can work together when teams build, test, and release in a shared flow. DevSecOps SDLC practices add security checks to that flow, rather than leaving them until release week.
Documentation and Scrum in the secure SDLC
SDLC documentation records what the team planned, checked, changed, and approved. Useful records include security needs, threat models, test results, risk decisions, release notes, and incident findings. Keep records close to the work so people can find them later.
Good records help new team members understand why a control exists. They also help reviewers check whether the team met its own rules. A record should be brief, dated, and linked to an owner or decision.
Scrum SDLC work fits security tasks into the product backlog and each sprint. The team can add threat review, code checks, or security tests to the work for a feature. The product owner and team should agree on what counts as done.
SDLC and Scrum are not competing methods. Scrum guides how a team plans and delivers work, while a secure SDLC sets security work across the product's life. Include security tasks in planning, daily work, review, and later upkeep.
Teams should review their records and checks when risks change. A new data type, outside service, or user group can change what needs protection. Make the update part of the work, not a separate paperwork drive.
Best practices for effective secure SDLC work
Begin with the risks that matter most to users and the business. Set a few clear rules, assign owners, and make sure the team knows when to pause a release. A small process that teams follow is stronger than a large one that they ignore.
- Set security goals early. Name sensitive data, likely threats, and the people who approve risk.
- Build checks into the workflow. Run code and package checks during normal development.
- Test based on risk. Spend more time on features that protect sensitive data or key services.
- Track fixes to closure. Give each issue an owner, a due date, and a clear status.
- Learn from incidents. Update tests and design rules when a real flaw reveals a gap.
Review the process at a steady pace. Track whether teams fix high-risk issues before release and whether repeat problems decline. Use those results to adjust the checks, training, and records.
The aim is not more paperwork or more tools. The aim is safer software, with clear proof of how the team made it safer. Keep the process useful, repeatable, and matched to the product's risk.
Frequently asked questions
What does SDLC stand for?
SDLC stands for software development lifecycle. It covers the work of planning, building, testing, releasing, and maintaining software.
What is a secure SDLC?
A secure SDLC adds security goals and checks to each stage of software development. It helps teams find risks early and respond to flaws.
How does Scrum fit into the SDLC?
Scrum helps teams plan and deliver work in short sprints. Teams can add threat reviews, code checks, and security tests to each sprint.
Which tools support a secure SDLC?
Common tools scan source code, test running services, review third-party packages, and find exposed secrets. Work tracking tools also help assign fixes and record decisions.
Why is SDLC documentation important?
It records security needs, test results, risk choices, and approvals. These records help teams review decisions and maintain software over time.